Defining a robust GitHub Copilot enterprise policy has become urgent for IT managers in 2026. With GitHub reporting over 1.8 million enterprise Copilot seats active globally, most large organisations now have developers using AI code generation — often before any formal GitHub Copilot enterprise policy exists. The gap between adoption and governance creates serious risks: intellectual property exposure, security vulnerabilities injected into codebases and EU AI Act compliance obligations for organisations subject to its high-risk system provisions.
The security evidence is unambiguous. A 2023 empirical study published in ACM TOSEM found that 35.8% of Copilot-generated code snippets contain security weaknesses spanning 42 different Common Weakness Enumeration (CWE) categories. A Stanford University study found that developers using AI assistants were not only more likely to produce insecure code — they were also more confident that their insecure code was secure, a false-confidence effect that makes AI-assisted security vulnerabilities harder to catch in review.
And the Verizon DBIR 2025 reports a median 94-day window between a secret being leaked in a GitHub repository and its remediation — a timeline that makes automated secret scanning non-negotiable.
This guide provides a five-rule framework for building a GitHub Copilot enterprise policy that balances developer productivity with legal, security and compliance requirements.
Without a GitHub Copilot enterprise policy, individual developers make decisions that carry enterprise-level consequences. Copilot suggestions trained on public code repositories can reproduce copyrighted snippets — Microsoft’s 2023 lawsuit settlement acknowledged this risk. Additionally, Copilot can generate insecure code patterns: a Stanford study found AI-assisted developers were more likely to introduce security vulnerabilities in authentication and cryptography code when they did not critically review suggestions.
Furthermore, the EU AI Act classifies AI systems used as safety components of software products or in high-risk deployment contexts as potentially high-risk. If your organisation develops software for healthcare, financial services or critical infrastructure, your GitHub Copilot enterprise policy must address AI Act classification before the August 2026 enforcement deadline. Unmanaged shadow AI use — developers using Copilot outside IT-sanctioned channels — compounds all these risks.
With GitHub Copilot surpassing 20 million users in July 2025 and deployed across 90% of the Fortune 100, ad-hoc developer adoption has outpaced policy creation in most enterprises. Your GitHub Copilot enterprise policy must specify where Copilot is permitted and where it is not. A clear use-case matrix prevents ambiguity and gives developers actionable guidance.
Permitted use cases (typical enterprise policy):
Restricted or prohibited contexts:
Therefore, publish this matrix in your developer handbook and enforce it through code review checklists rather than relying solely on technical controls.
GitHub Copilot is trained on publicly available code, including GPL, AGPL and other copyleft-licensed repositories. A well-designed GitHub Copilot enterprise policy must address the risk that Copilot suggestions reproduce licensed code that your organisation cannot legally incorporate into proprietary products.
Practical controls:
Moreover, consult your legal team on whether your jurisdiction requires disclosure of AI-generated code in software supply chain documentation — the EU Cyber Resilience Act’s software bill of materials (SBOM) requirements may apply.
A GitHub Copilot enterprise policy that does not address security is incomplete. Copilot optimises for plausibility, not security — it will confidently suggest insecure patterns if they appear frequently in its training data. However, this risk is manageable with the right controls.
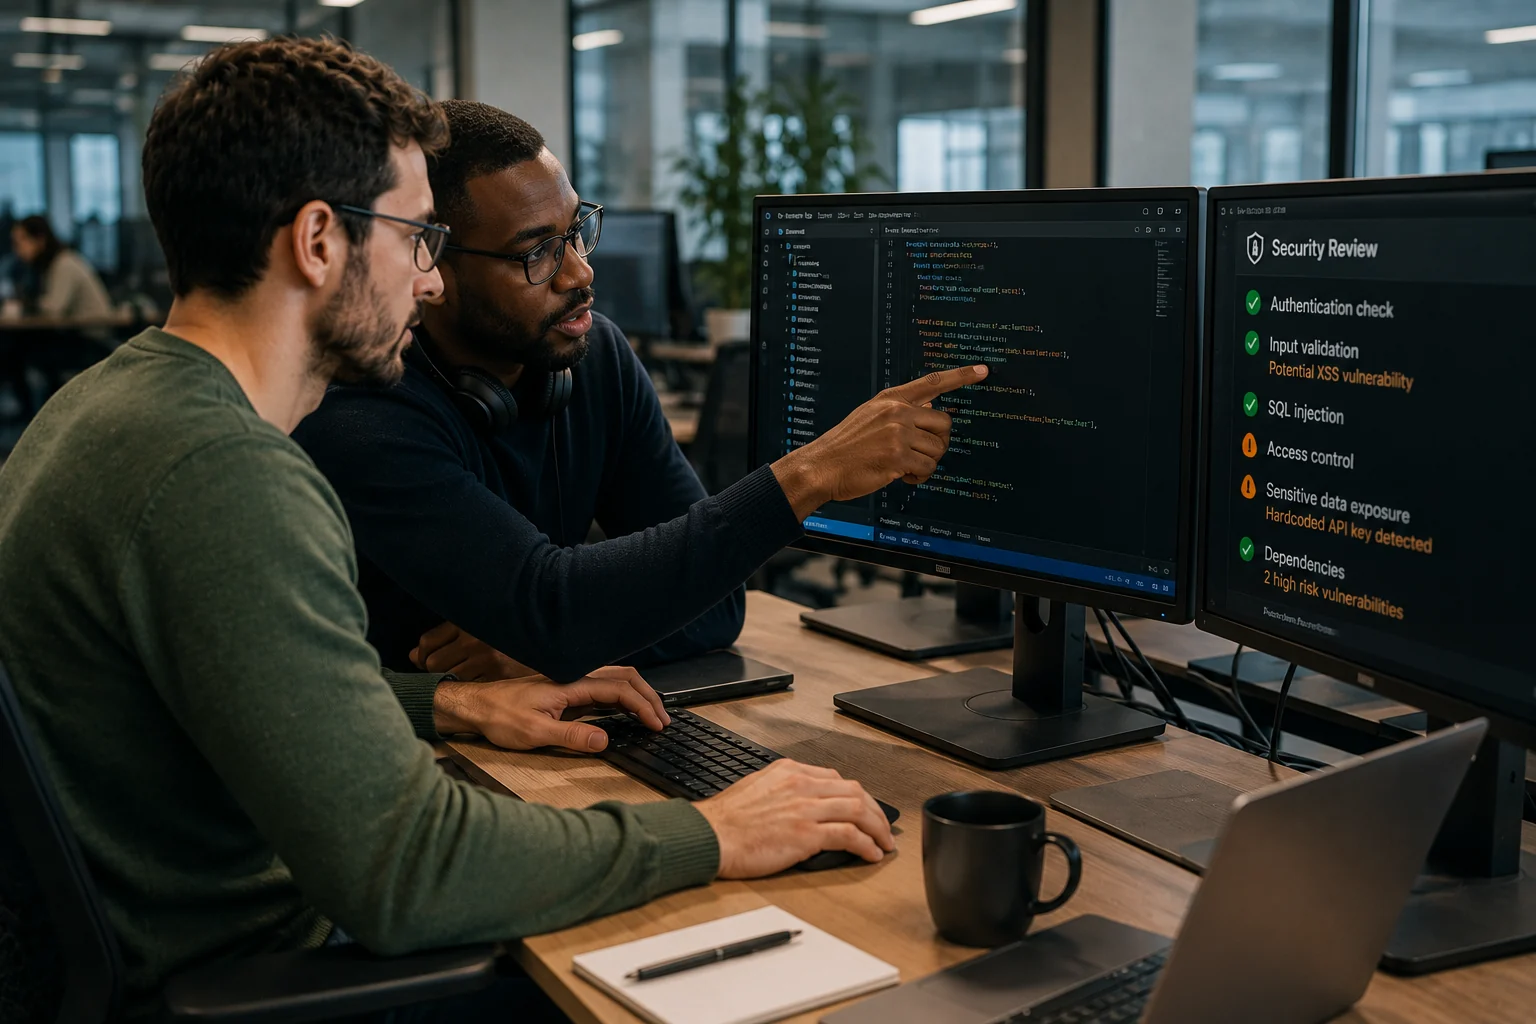
Mandatory security controls to include in your GitHub Copilot enterprise policy:
Connecting your GitHub Copilot enterprise policy to your AI-powered security operations workflow creates a closed loop: vulnerabilities introduced in development are caught by runtime detection before they reach production.
By default, GitHub Copilot may use prompts, suggestions and user engagement data to improve its models. For enterprise deployments, this creates GDPR and confidentiality risks if developers expose proprietary code or personal data through Copilot prompts.
Your GitHub Copilot enterprise policy must mandate:
Furthermore, review your EU AI Act enterprise compliance obligations to determine whether Copilot’s use in your organisation requires a formal DPIA under GDPR Article 35, particularly if used to process code involving personal data.
A GitHub Copilot enterprise policy is only as effective as its enforcement. Consequently, assign clear ownership: an AI tool owner (typically the CISO or CTO office) who is accountable for policy updates, exception management and compliance monitoring.
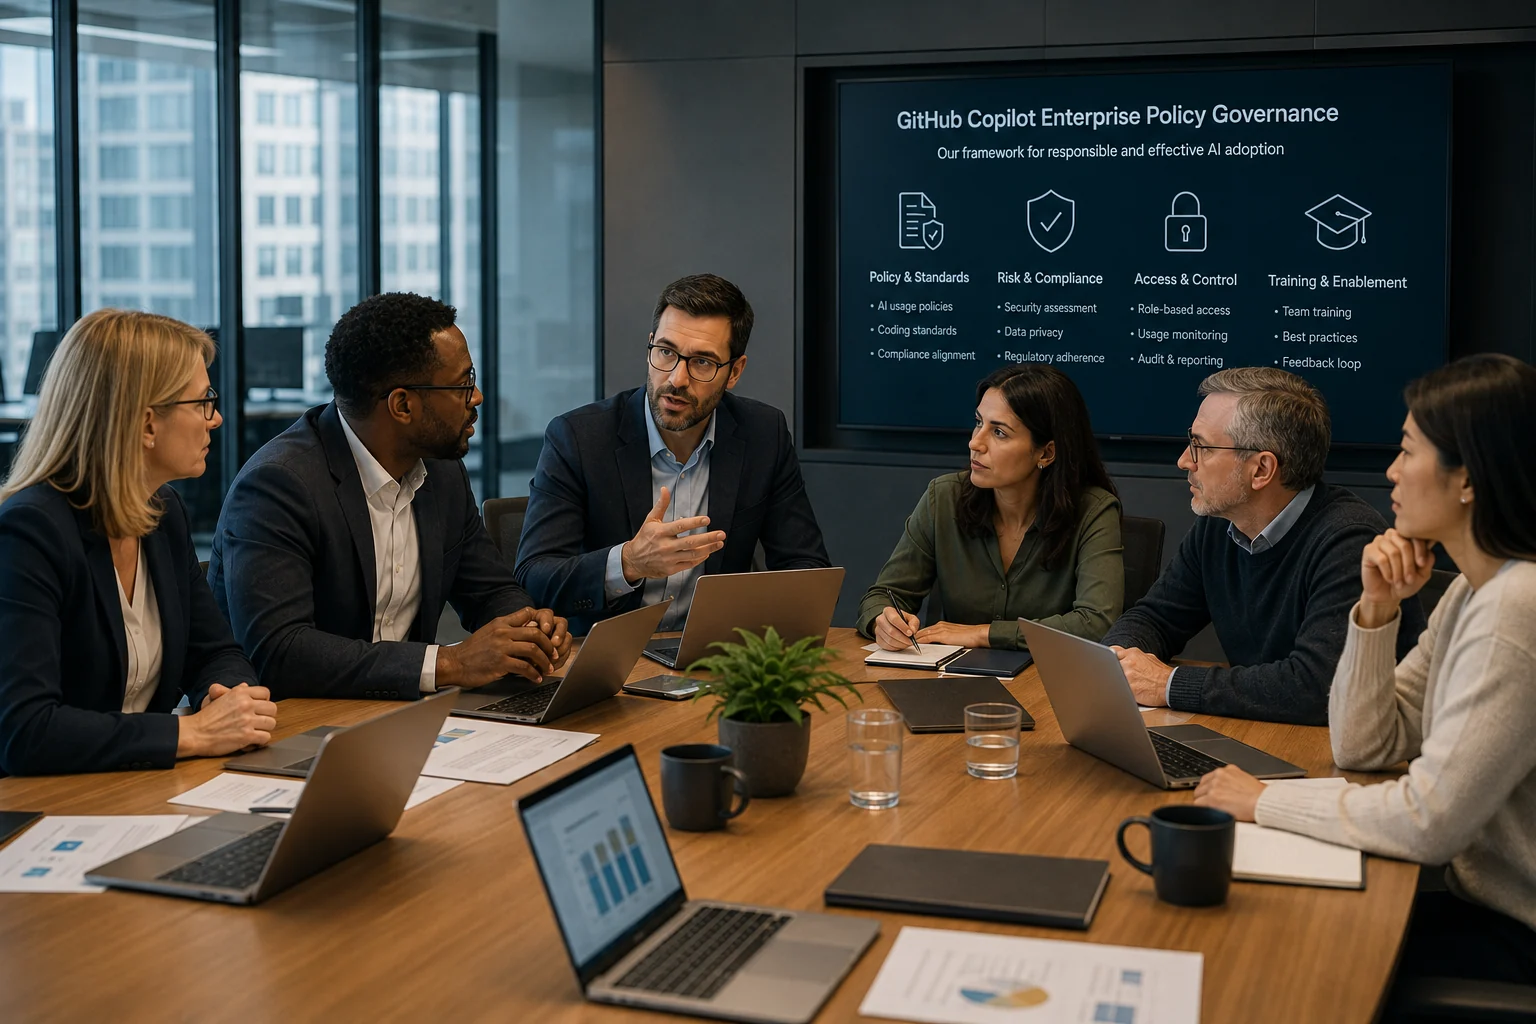
Governance components your policy must include:
Finally, integrate your GitHub Copilot enterprise policy into your broader AI governance framework. As shadow AI risk expands beyond code generation to document drafting, data analysis and customer interaction, Copilot policy becomes one component of an enterprise-wide AI tool governance programme.
Yes, in specific circumstances. If your organisation develops software in regulated sectors (healthcare, financial services, critical infrastructure, law enforcement, education) and uses Copilot to generate code for systems in those sectors, the EU AI Act’s high-risk classification may apply to the resulting AI-assisted software. Your GitHub Copilot enterprise policy should include an AI Act risk screening step for all projects in regulated domains. Additionally, GPAI obligations apply to any organisation fine-tuning or deploying foundational models — using GitHub Copilot as a service does not trigger these, however building custom coding assistants on top of open-weight models would.
For enterprise policy compliance, the Copilot Enterprise tier is strongly recommended. It is the only tier that provides: organisation-wide policy controls and audit logs, Copilot chat grounded in your internal codebase (reducing external data exposure), advanced duplication detection for IP protection and the contractual terms (DPA, IP indemnity) required for enterprise compliance programmes. Copilot Business covers the core controls. The Individual tier lacks the administrative controls needed for an enforceable GitHub Copilot enterprise policy and should not be used on company accounts.
Your GitHub Copilot enterprise policy must explicitly address third-party developers. Contractors working in your GitHub organisation should be provisioned and deprovisioned through your central IdP exactly like employees — no informal seat sharing. Your master services agreements and NDAs with development partners should be updated to reference your AI tool usage policy and prohibit use of Copilot or similar tools on your codebase without written approval. According to GitHub’s enterprise administration documentation, organisation owners can restrict Copilot access to specific teams, allowing you to exclude contractors from Copilot access entirely if your policy requires it.
Effective policy governance requires measurable outcomes. Track these key indicators: Copilot code acceptance rate by team (a signal of suggestion quality and developer trust), SAST findings per 1,000 lines on AI-assisted versus non-AI-assisted code (measures security impact), exception request volume (high numbers indicate policy friction or developer workarounds), confirmed IP or security incidents attributable to Copilot suggestions (the outcome metric that matters most) and training completion rates (a leading indicator of policy awareness). Review these metrics quarterly with your AI tool owner and security team to identify whether your GitHub Copilot enterprise policy is achieving its intended risk reduction.
Editorial disclosure: AI tools may have assisted research, drafting or editing. ITnovati remains responsible for the published text. Time-sensitive technical, legal and product claims should be checked against the linked primary sources.
 ITnovati