The EU Cyber Resilience Act enterprise implications are already taking shape. Adopted by the European Parliament in October 2024 and published in the Official Journal of the EU in November 2024, the CRA is the first EU regulation to impose mandatory cybersecurity requirements on manufacturers and suppliers of hardware and software products with digital elements sold in the European market. EU Cyber Resilience Act enterprise obligations apply across three dimensions: secure-by-design requirements during product development, vulnerability handling obligations throughout the product lifecycle, and incident reporting duties once products are in operation.
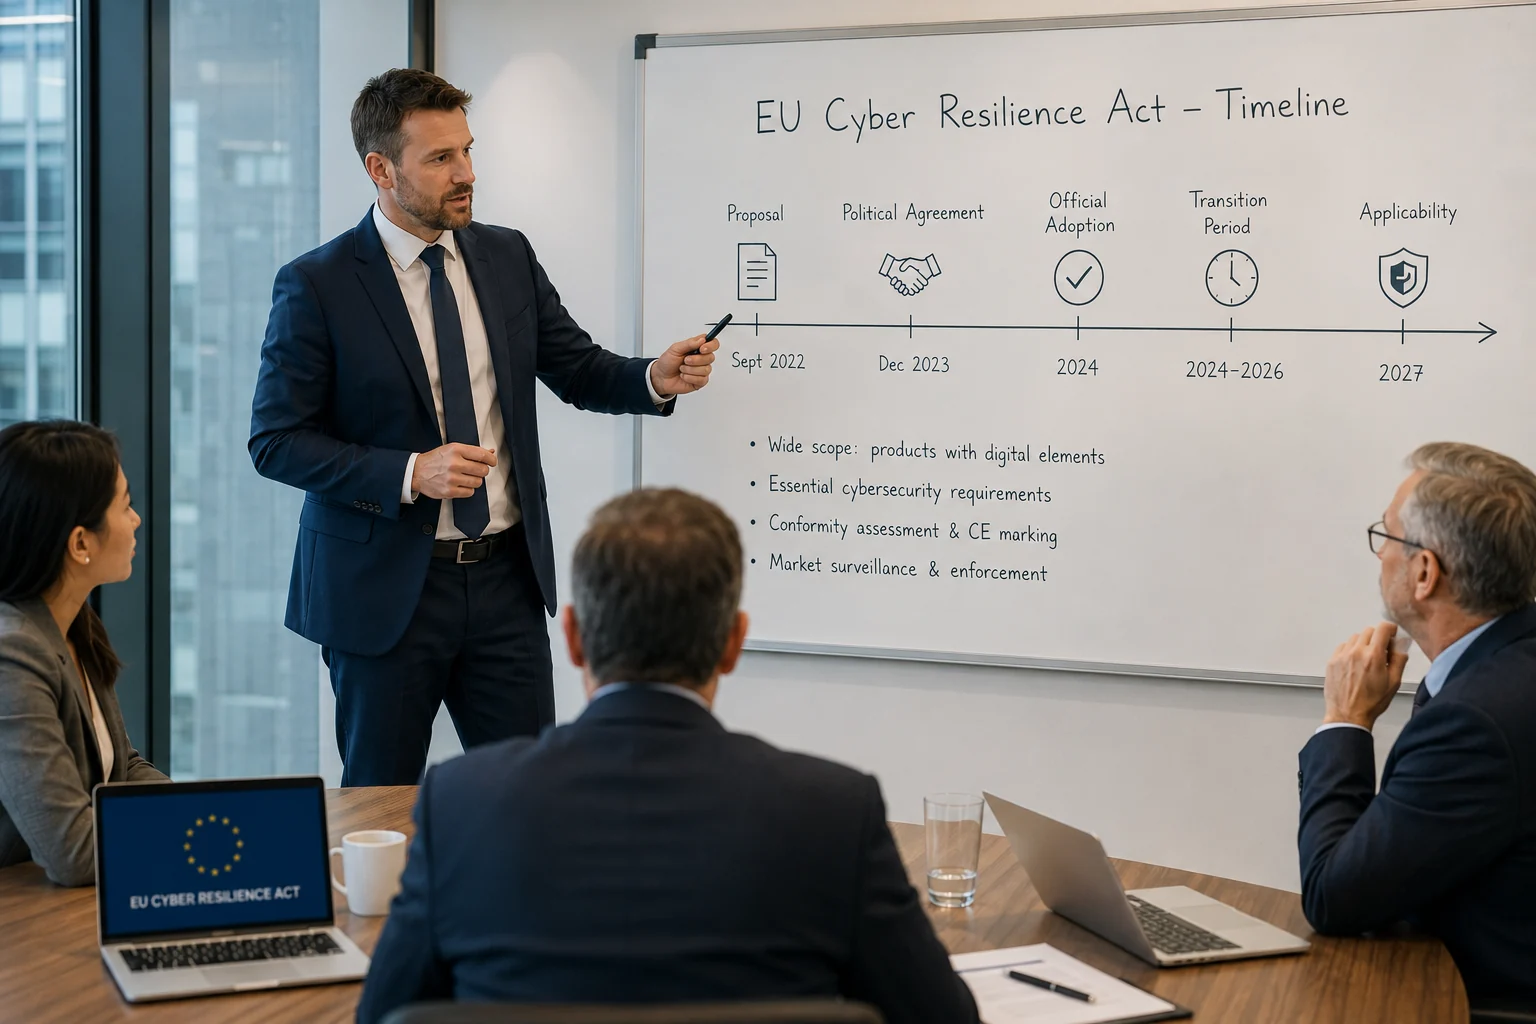
The timeline is more compressed than many organisations realise. While full application of the EU Cyber Resilience Act enterprise requirements takes effect in December 2027, the notification body and market surveillance provisions begin applying in June 2026 — meaning that companies planning product launches or major software releases in 2026 must already be building compliance into their development and procurement processes today. Additionally, ENISA is developing harmonised European standards throughout 2025 and 2026 that will define what “appropriate cybersecurity” means in practice for each product category.
Understanding whether your organisation falls within EU Cyber Resilience Act enterprise scope is the first compliance step. The CRA applies to any product with digital elements placed on the EU market — broadly defined to include any software or hardware item that can connect to a device or network. This encompasses numerous types of enterprise products: routers, firewalls, operating systems, enterprise software suites, IoT devices, industrial control systems, and consumer-facing connected products manufactured or sold by European companies.
The CRA distinguishes between three risk tiers. Default products — the large majority of connected devices and software — must self-certify compliance against the CRA’s essential requirements. Important class I products — including identity management software, network management tools, VPNs, password managers, and industrial automation systems — require third-party involvement or conformity assessment against harmonised standards. Important class II products — including operating systems, industrial control systems with safety functions, and hypervisors — require mandatory third-party conformity assessment by a notified body. For enterprise IT teams responsible for product procurement, EU Cyber Resilience Act enterprise classification of every vendor’s product in your supply chain is a new due diligence requirement.
Software-only products sold under licence are included in scope. However, open-source software developed outside a commercial context is excluded — with important caveats. If your organisation monetises, distributes, or provides commercial support for open-source components, those components may fall within EU Cyber Resilience Act enterprise scope regardless of their open-source licence. Furthermore, cloud services are excluded from the CRA itself but are addressed through NIS2 and the EU AI Act for AI-powered cloud products.
The EU Cyber Resilience Act enterprise essential requirements in Annex I define the technical baseline every in-scope product must meet. These requirements are more specific and operationally demanding than previous EU product safety legislation.
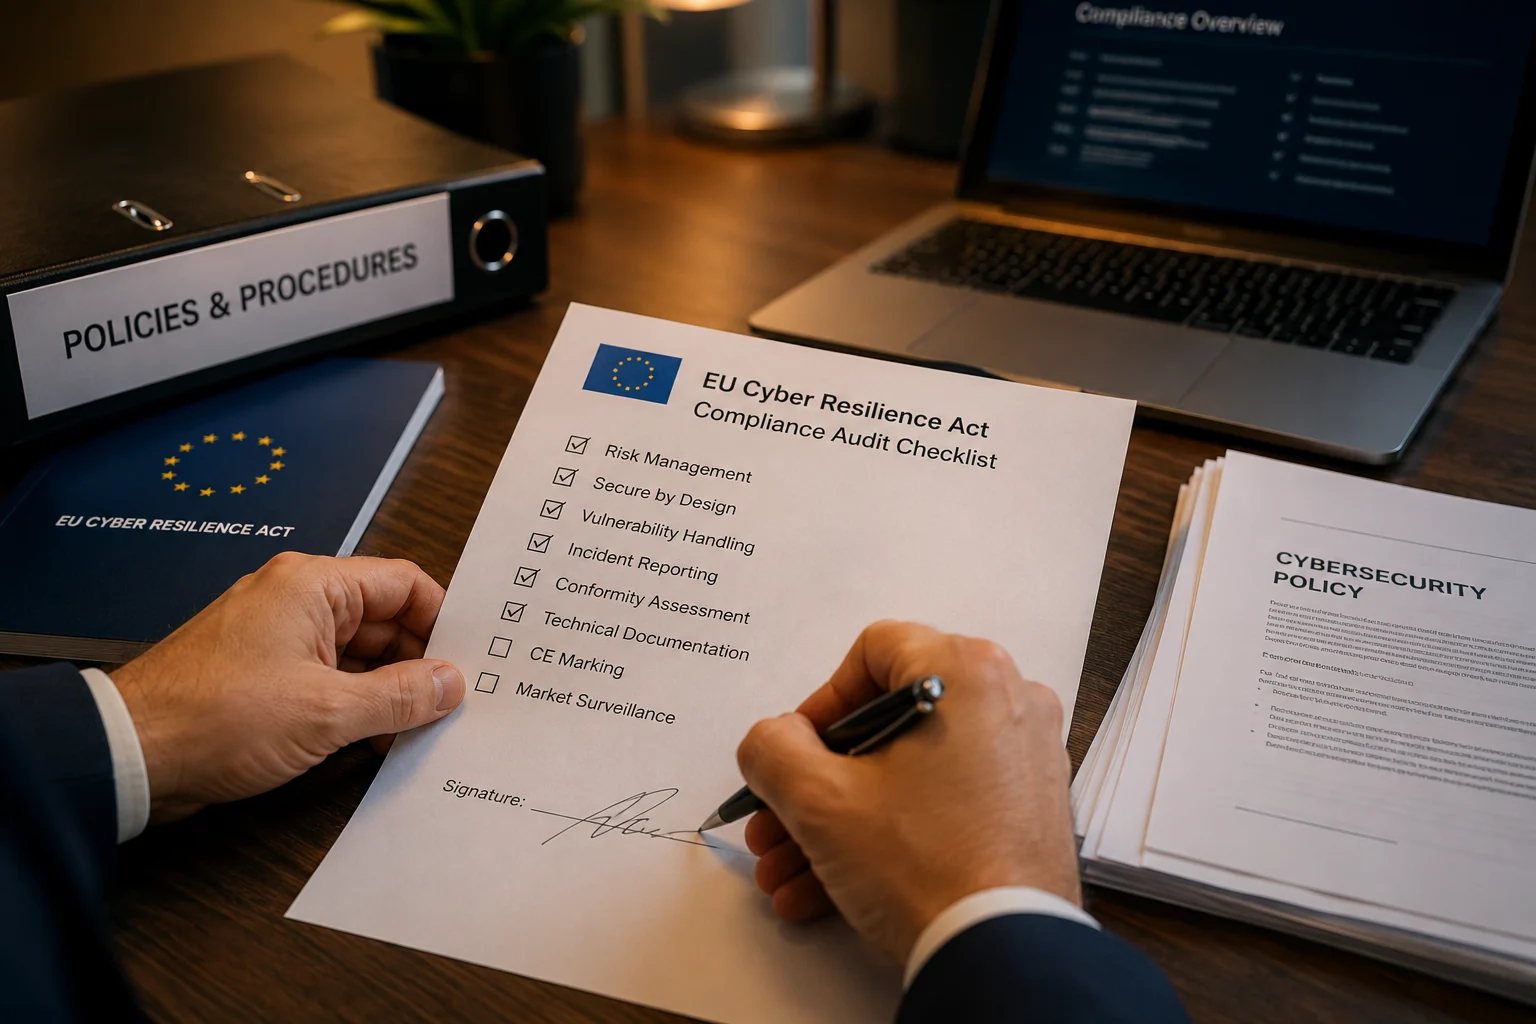
Products must ship without known exploitable vulnerabilities. This means manufacturers must conduct thorough security testing before market release — including penetration testing, code review, and dependency scanning — and cannot ship a product containing CVEs rated critical or high without documented remediation or accepted risk. For enterprise software vendors, this requirement fundamentally changes the release gate process.
Secure default configurations are mandatory. Products must be deployable securely without requiring users to reconfigure security settings. Default passwords are prohibited; authentication must be enabled by default; unnecessary services and interfaces must be disabled out of the box. Enterprise procurement teams should update vendor questionnaires to require CRA-compliant default configuration documentation.
Vulnerability disclosure and handling is codified as a legal obligation. Manufacturers must establish and publish a vulnerability disclosure policy, respond to vulnerability reports from external researchers, and patch critical vulnerabilities within defined timelines. Moreover, actively exploited vulnerabilities must be reported to ENISA and the relevant national CSIRT within 24 hours of discovery — the same timeline as NIS2’s early warning obligation.
Software bill of materials (SBOM) documentation is required for all in-scope products. Manufacturers must maintain a machine-readable SBOM identifying all third-party and open-source components, their versions, and their known vulnerabilities. Consequently, enterprise procurement processes must now request and verify SBOM documentation from software vendors as part of standard vendor onboarding.
The EU Cyber Resilience Act enterprise supply chain impact is potentially the most significant compliance challenge for large organisations. Most enterprise software environments depend on dozens of vendors whose products will need CRA compliance by December 2027. However, the conformity assessment requirements for class I and class II products mean that some vendors will require 18 to 24 months to complete third-party assessments — making 2025 the effective start date for compliance preparation, not 2026.
Major enterprise software and hardware vendors — Microsoft, SAP, Siemens, Cisco — have already published CRA readiness statements and begun adapting their development and disclosure practices. Smaller independent software vendors face a more acute challenge: the cost of third-party conformity assessment for class I products is estimated between €30,000 and €100,000 per product, which is material for mid-size software companies with product portfolios of ten or more items.
For enterprise procurement teams, the EU Cyber Resilience Act enterprise due diligence obligation is practical and immediate: update vendor onboarding questionnaires to capture CRA classification, conformity assessment status, SBOM availability, and vulnerability disclosure policy. Vendors who cannot answer these questions by 2026 represent supply chain risk. For broader cybersecurity and regulatory context, see our guides on NIS2 compliance, EU AI Act compliance, and shadow AI risk.
Explore our full AI coverage and IT management resources.
EU Cyber Resilience Act enterprise preparation requires action across product development, procurement, and vendor management — beginning now, not in 2027.
The EU Cyber Resilience Act enterprise requirements apply in phases. Notification body and market surveillance provisions take effect in June 2026. Vulnerability and incident reporting obligations apply from September 2026. Full application of all EU Cyber Resilience Act enterprise essential requirements — including secure-by-design, default configuration, and SBOM obligations — takes effect in December 2027. Organisations developing or procuring software and hardware for EU markets must begin compliance preparation now to meet these timelines.
Cloud services as such are excluded from EU Cyber Resilience Act enterprise scope — they are addressed by NIS2. However, software components delivered as part of a cloud product, on-premises software, or hybrid deployments may fall within CRA scope depending on how they are licensed and distributed. AI-powered cloud products are additionally subject to the EU AI Act’s GPAI and high-risk provisions. Enterprises should assess each product and service in their environment individually rather than assuming blanket exclusions.
EU Cyber Resilience Act enterprise penalties are structured by violation type. Non-compliance with the Annex I essential cybersecurity requirements — the core secure-by-design and vulnerability handling obligations — carries fines of up to €15 million or 2.5 percent of global annual turnover, whichever is higher. Non-compliance with other CRA obligations carries fines up to €10 million or 2 percent of global turnover. Providing incorrect or misleading information to market surveillance authorities carries fines up to €5 million or 1 percent of global turnover.
Editorial disclosure: AI tools may have assisted research, drafting or editing. ITnovati remains responsible for the published text. Time-sensitive technical, legal and product claims should be checked against the linked primary sources.
 ITnovati