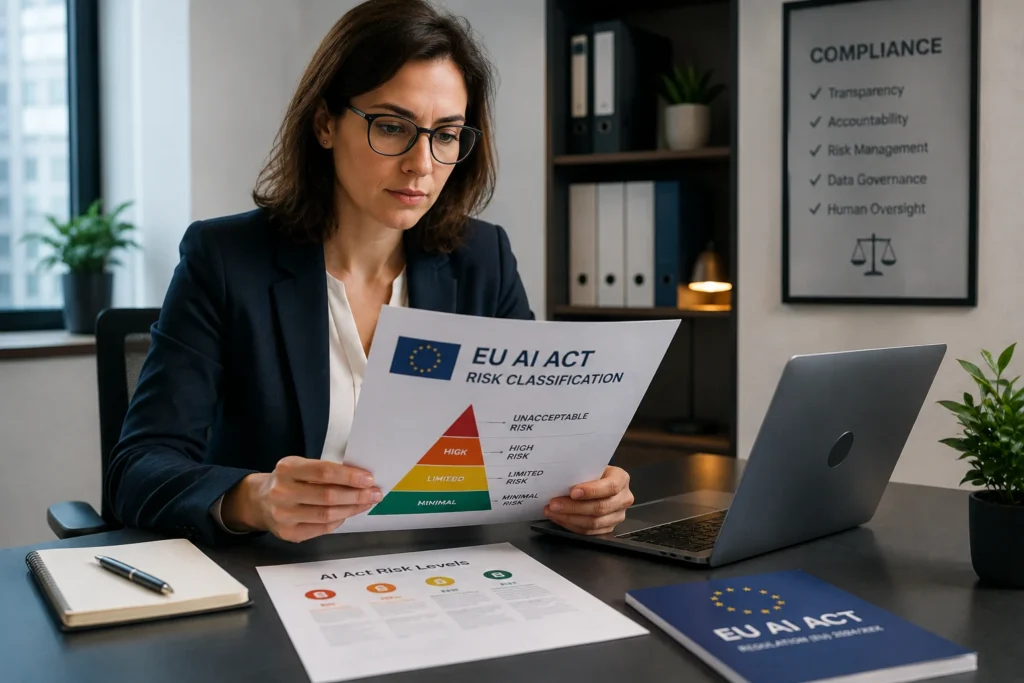
AI Act risk classification starts with the system’s intended purpose and the role of the organisation—not with the model name. A general chatbot, a recruitment-ranking tool and an AI safety component can use similar technology while carrying very different obligations.
For programme ownership and evidence controls, use the companion enterprise compliance checklist.
The common four-level summary—unacceptable, high, transparency or minimal risk—is useful for orientation, but the legal analysis is more precise. General-purpose AI has a separate track, exceptions and role changes matter, and a system can be subject to privacy, employment or product law even when it has no specific high-risk duties under the AI Act.
Screen the intended and reasonably foreseeable use against the prohibited practices in Article 5. These include defined forms of manipulation, exploitation, social scoring and certain biometric uses. The prohibitions are specific and include conditions and exceptions; shorthand such as “all biometric identification is banned” is inaccurate.
There are two principal routes. Annex I covers AI used as a safety component of, or itself constituting, products governed by listed EU product-safety legislation. Annex III covers specified use cases in areas such as biometrics, critical infrastructure, education, employment, essential services, law enforcement, migration and justice.
Matching a broad sector is not enough. Document the exact function, affected decision and any applicable exception. For example, an administrative HR tool is not necessarily classified the same way as a system used to rank candidates.
Article 50 applies from 2 August 2026. Depending on the system, providers or deployers may need to inform people that they are interacting with AI, support detection through machine-readable marking, or disclose deepfakes and certain AI-generated public-interest content. Apply the detailed conditions rather than labelling every AI-assisted output identically.
Providers of general-purpose AI models have model-level obligations, with additional duties for models with systemic risk. An enterprise using a third-party model still needs to assess its own deployment. Fine-tuning, substantial modification or placing a system on the market under a new name can change the organisation’s role.
Prohibited practices and AI-literacy duties have applied since February 2025. General-purpose AI governance obligations have applied since August 2025, and Article 50 transparency duties since 2 August 2026. Under the current revised timeline, high-risk rules for Annex III systems are scheduled from 2 December 2027 and rules for AI embedded in regulated products from 2 August 2028.
When classification is uncertain or the system affects rights, safety or access to essential services, obtain case-specific legal advice before deployment.
This article provides general information and is not legal advice.
Editorial disclosure: AI tools may have assisted research, drafting or editing. ITnovati remains responsible for the published text. Time-sensitive technical, legal and product claims should be checked against the linked primary sources.
 ITnovati